Computer security
Thema UR
Cloud et Cybersécurité, la bataille est lancée ? Le débat d'experts d'OVH, BitDefender et un Avocat
Cloud and Cybersecurity, the battle has begun? The experts' debate of OVH, BitDefender and a Lawyer
★
★
★
★
☆
4/5

(TR05) (INCYBER) Patrimoine informationnel : nouveaux défis face au Shadow AI
(TR05) (INCYBER) Information heritage: new challenges in the face of Shadow AI
★
★
★
★
☆
4/5

(TR05) (CFI) OT : la résilience des infrastructures critiques, un impératif géopolitique
(TR05) (CFI) OT: resilience of critical infrastructures, a geopolitical imperative
★
★
★
★
☆
4/5

(TR03) (INCYBER) Détection des menaces : orchestrer l’écosystème de sécurité
(TR03) (INCYBER) Threat detection: orchestrating the security ecosystem
★
★
★
★
☆
4/5
(TR01) (CFI) Cyber-résilience et robustesse industrielle : la continuité métier à l’épreuve...
(TR01) (CFI) Cyber-resilience and industrial robustness: business continuity put to the test...
★
★
★
★
☆
4/5

(T26) (CFI) Cyber OT 2026 : Anticiper la tempête – Réglementation, convergence IT-OT et résilience..
(T26) (CFI) Cyber OT 2026: Anticipating the Storm – Regulation, IT-OT Convergence and Resilience.
★
★
★
★
☆
4/5

(P01) (INCYBER) Sommet d’ouverture - Keynote Henna Virkkunen
(P01) (INCYBER) Opening Summit - Keynote Henna Virkkunen
★
★
★
☆
☆
3/5
(P01) (INCYBER) Sommet d’ouverture - Interview Olivier Gavalda
(P01) (INCYBER) Opening Summit - Interview Olivier Gavalda
★
★
★
★
☆
4/5
(P01) (INCYBER) Sommet d’ouverture - Andy Yen (Proton) & Octave Klaba (OVHCloud)
(P01) (INCYBER) Opening Summit - Andy Yen (Proton) & Octave Klaba (OVHCloud)
★
★
★
★
☆
4/5
(OUVERTURE) (CFI) Cybersécurité industrielle : entre maîtrise des risques et compétitivité durable
(OPENING) (CFI) Industrial cybersecurity: between risk management and sustainable competitiveness
★
★
★
★
☆
4/5
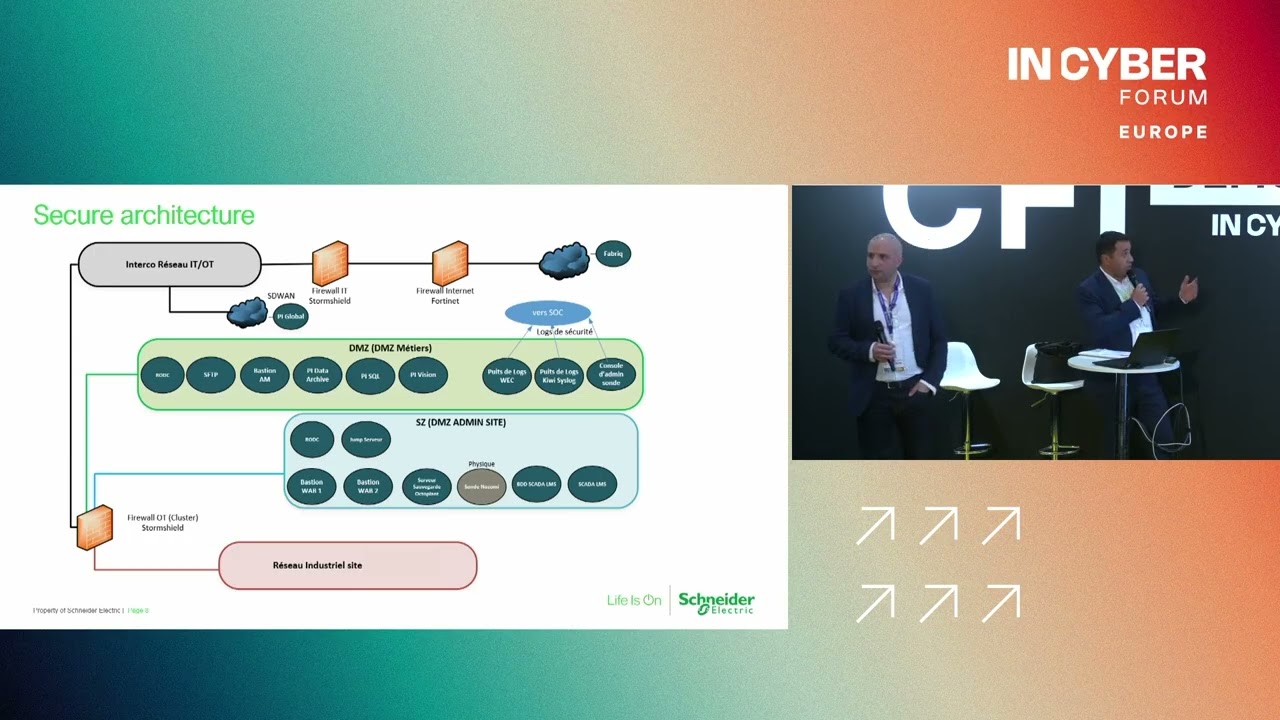
(DT10) (CFI) Cybersécurité et Digitalisation, Sécuriser la Data pour Maximiser la Valeur à l'ère...
(DT10) (CFI) Cybersecurity and Digitalization, Securing Data to Maximize Value in the Era...
★
★
★
☆
☆
3/5
(DT05) (CFI) RSSI : trop de conformité, pas assez de sécurité - quand l’empilement réglementaire...
(DT05) (CFI) RSSI: too much compliance, not enough security - when the regulatory stack...
★
★
★
★
☆
4/5

(DT04) (CFI) Risque cyber de la supply chain : de l’exposition systémique au reverse stress...
(DT04) (CFI) Cyber risk of the supply chain: from systemic exposure to reverse stress...
★
★
★
★
☆
4/5
(CHALLENGE) (CFI) Challenge Cyber4OT Advens & CESIN
(CHALLENGE) (CFI) Cyber4OT Challenge Advens & CESIN
★
★
★
★
☆
4/5

(C18) (INCYBER) CH de Pontarlier x Databack : Retour d’expérience sur la gestion d’un incident...
(C18) (INCYBER) CH of Pontarlier x Databack: Feedback on managing an incident...
★
★
★
★
☆
4/5

(C07) (INCYBER) Sécuriser la chaîne d’approvisionnement du Logiciel et de l'IA: L'approche de Google
(C07) (INCYBER) Securing the Software and AI Supply Chain: Google's Approach
★
★
★
★
☆
4/5

(C01) (INCYBER) Réussir sa transition vers l’Agentic SOC: le guide pratique par Google et I-TRACING
(C01) (INCYBER) Succeeding in your transition to Agentic SOC: the practical guide by Google and I-TRACING
★
★
★
★
☆
4/5

Solving Prompt Injection & Shadow AI for AI Malware
★
★
★
★
☆
4/5

CISO mini interviews at RSAC 2026
★
★
★
☆
☆
3/5


0x737 - Teknik - Trivy... part 2 ou comment le supply chain est LE vecteur
0x737 - Teknik - Trivy... part 2 or how the supply chain is THE vector
★
★
★
★
☆
4/5


Pour une poignée de data : sécuriser l’or numérique à l’ère des menaces hybrides
For a Fistful of Data: Securing Digital Gold in the Era of Hybrid Threats
★
★
★
★
☆
4/5

Dépendances numériques : comment bâtir un écosystème de confiance ?
Digital dependencies: how to build a trust ecosystem?
★
★
★
★
☆
4/5

¡Claude code filtrado! ¿Qué se filtró, cómo se filtró y qué significa para Anthropic?
Claude code leaked! What was leaked, how was it leaked, and what does it mean for Anthropic?
★
★
★
★
☆
4/5


NoLimitSecu #537 - Recherche de compromission avancée sur mobile
NoLimitSecu #537 - Advanced compromise research on mobile
★
★
★
★
☆
4/5

RSAC Conference Frontier Award
★
★
★
☆
☆
3/5